
Claims Fraud Fairness Reviews
Are some customers more likely to be flagged, investigated or declined?
- Fraud detection rules and models decide which claims your team triages and investigates.
- Rules get added and changed over the years, and the data feeding them changes too.
- If they're off, investigators spend time on the wrong claims.
- Genuine customers wait longer, and some groups may be treated unfairly.
We review the rules and models, then test claims data for impact.
When it's worth checking (if any of these apply):
- You haven't yet specifically checked whether the rules and models are fair.
- Your rules or models use protected data like race, gender, age, or disability.
- Your rules or models use proxies like postcode, licence type or lodgement channel.
- Your board, a regulator or your team has asked whether the process treats some customers unfairly.
- Investigators say too many referrals are wasting their time.
- You use a vendor fraud tool and haven’t tested its results on your own customers.
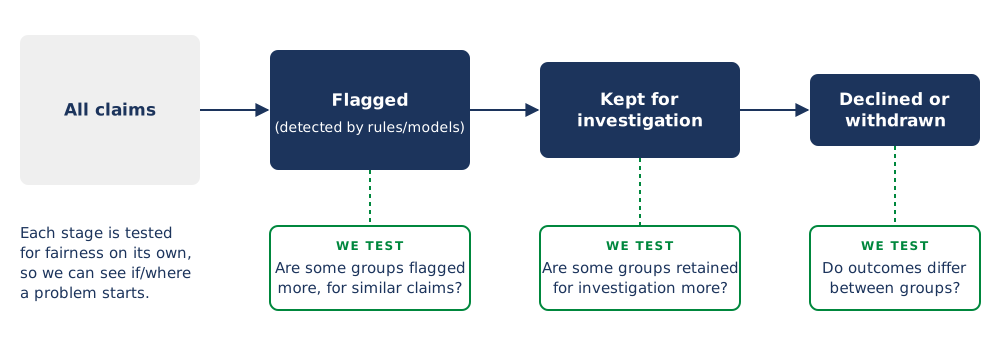
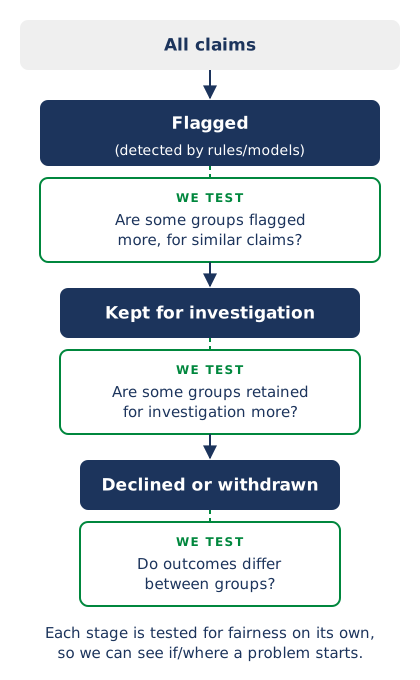
What we check
- Configuration and code: input data (including third-party data), rules and models.
- For protected attributes: race, gender, age, disability.
- For proxies: postcode, licence type, language, keywords.
- Claims data for a defined period, checking for adverse impact.
What you get
- A clear result for each test: within bounds (a gap may exist, but it's small enough to accept), outside bounds, or not enough information to say.
- Where in the models and rules there is potential for bias (regardless of the actual data).
- A short summary for your executive team, plus the detail you need to fix any issues.
What happens in a review
- Agree the scope, the products and the analysis period.
- Understand the process, rules, models and data sources, through discussions and document reviews.
- Model review: go through the code and model documentation to identify any use of protected attributes, directly or through proxies, and confirm any exceptions.
- Impact review: analyse claims data for differences between groups. We start with a sample period to get the extract right and work out how much data a reliable result needs, then run the analysis on the full period.
- Report the results and opportunities for improvement.
Working with us
Timeframe
Most reviews take
2 to 6 months.
Fixed price
The typical range is
$50k to $150k (AUD).
Senior only
Work with Yusuf directly.
No junior staff.
Independent
We don't design or build
the systems we review.
Common Questions
We don't hold data on race or disability. Can you still test for bias?
Yes. We test the attributes you do hold, such as age and sex. We also check whether other data is acting as a stand-in.
If you find a gap, does that mean we're discriminating?
Not necessarily. A gap can have a legitimate explanation, such as age in certain jurisdictions. We work through each result with your team.
How much of our team's time does it take?
Most of it is at the start: a data extract, and time with the people who know how the process, rules and models work.
After that, we come back with questions as results come up.
(It usually takes less of your team's time than a typical review, because the person asking the questions is experienced.)
How to get started
If you're responsible for claims, or claims fraud specifically, and want to know it's fair, book a call.
We'll talk through your setup and whether a review makes sense.